Still have questions?
Speak to our team
The National Cyber Security Centre (NCSC) has just published a rather sobering assessment of how AI could shape cyber threats through 2028.
The October PHP vulnerability which led to millions of hacking attempts and global website outages is a warning for what is coming. Cyber criminals are using AI capability to exploit old code in software and with similar, but lower profile, incidents happening throughout this month, this could be the tip of the iceberg.
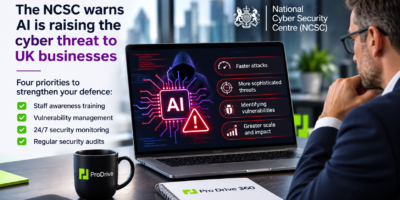 For Accountants, Lawyers and Financial Services firms, who all handle confidential client information, it is a clear signal that you need to act now.
Published on 3 November 2026, the assessment highlights:
Much of the assessment concerns national infrastructure. Our recommendations below apply its wider lessons to professional and financial services firms.
These are Pro Drive’s practical recommendations, not a checklist prescribed by the report.
| Priority | What effective protection looks like |
| Improve staff awareness | Provide practical training on suspicious requests, independently verifying payment changes and reporting concerns promptly, without blame. |
| Manage vulnerabilities properly | Identify security weaknesses, prioritise fixes by risk, assign responsibility and deadlines, and verify that fixes worked. Scanning alone is not enough. |
| Monitor security 24/7 | Monitor key systems around the clock, with clear arrangements for investigating alerts and responding outside office hours. |
| Audit regularly | Most important – regularly benchmark your environment against defined standards, identify gaps and track corrective work through to completion. |
Pro Drive clients who are subscribed to one of our security packages will have this already – and we are continually updating their protection.
Having security tools is not the same as knowing they work. Ask your IT provider to demonstrate:
Both cyber security tools and your Microsoft systems are being updated on a regular basis, usually at least monthly, to keep pace with the latest threats. Usually this requires and IT professional to update the configuration for you to receive the protection.
Audits support ongoing protection. They do not replace monitoring, maintenance or incident response.
These priorities sit within Pro Drive 360, our approach to governing and continuously improving IT.
We assess more than 200 operational, security and productivity factors, benchmark your environment against defined standards and review progress, risks and priorities quarterly.
The objective: to know where you stand, address the gaps and measure improvement rather than assume it.
Do not wait for an incident to discover where protection is missing.
Book an IT review with Pro Drive IT to benchmark your current cyber security and identify what needs attention.
Speak to our team